Hi, to confirm your appointment you will be redirected to the dedicated booking form.

AI and Privacy: What Happens to the Data We Enter?

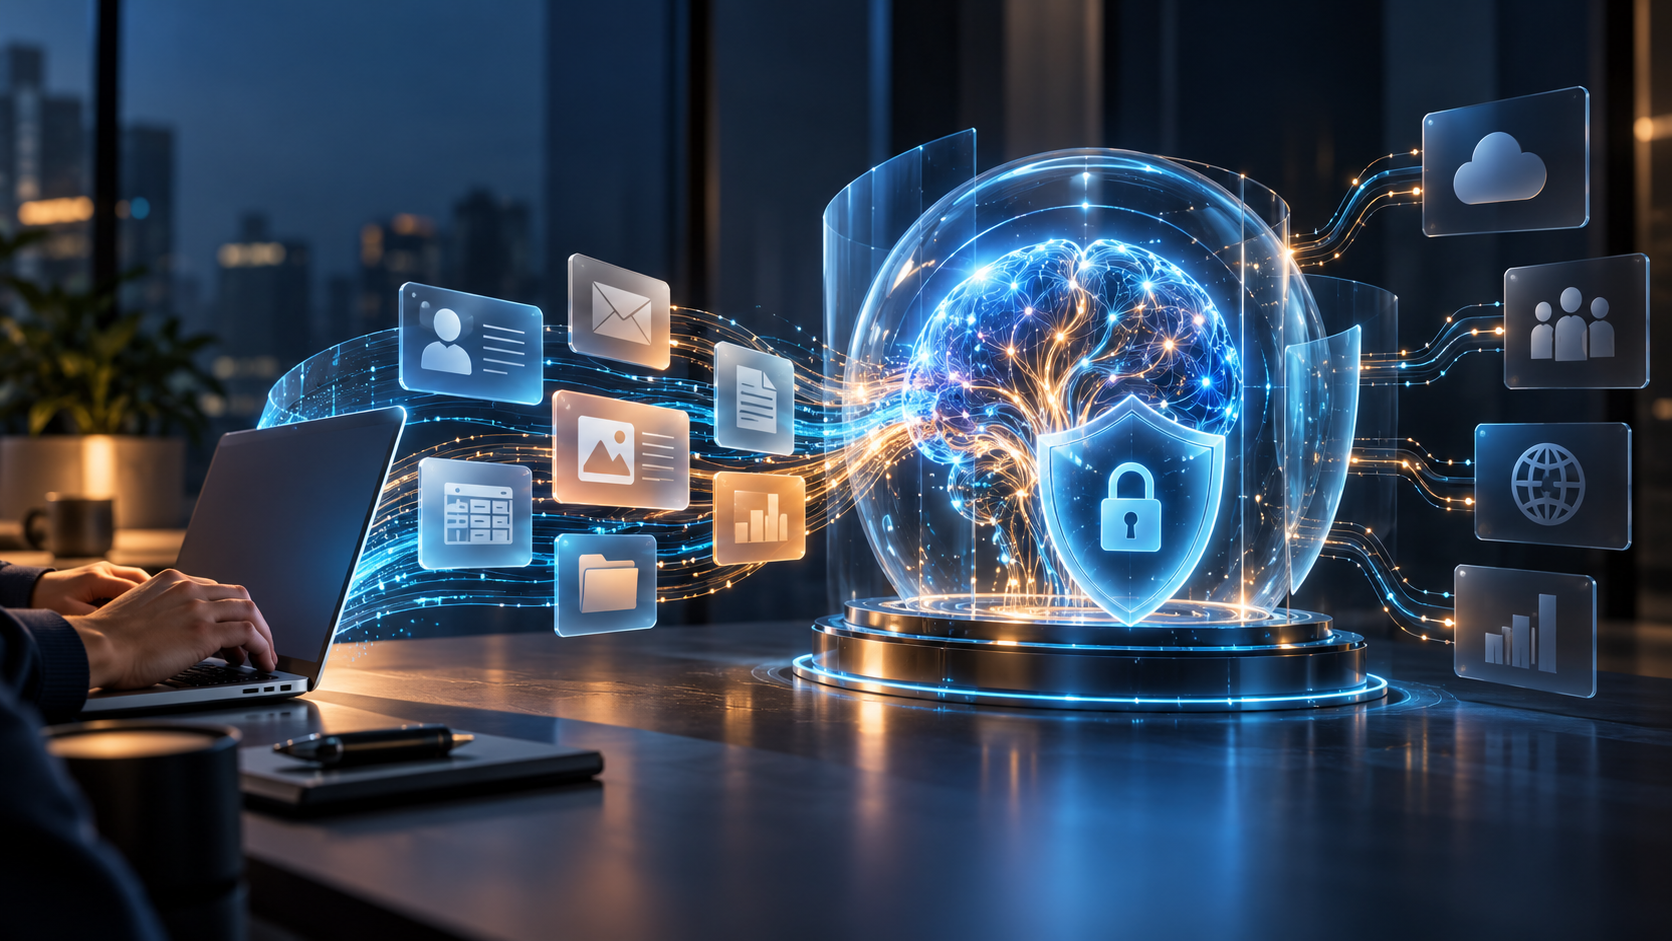
As we increasingly integrate artificial intelligence (AI) into our daily tasks, concerns about AI and privacy grow. Whether it’s entering an email into a chatbot, summarizing a contract, or uploading a medical report, the data we input into these AI systems often contains sensitive personal or business information. Understanding the journey of this data—where it goes, how it’s used, and who might access it—is crucial for both protecting our privacy and complying with legal standards like the General Data Protection Regulation (GDPR).
When you use an AI service, your data is transmitted to the provider’s systems where it undergoes processing necessary to generate the desired output. This might include storage of your data, integration with other services, and potentially, the use of your data to enhance the AI service itself. However, the specifics can vary significantly based on the type of service you’re using—be it a free consumer-grade service or a professional business solution accessed via APIs or executed locally.
Not all AI providers handle data in the same way. Some may store conversations and technical logs for varying periods, while others might use the content to improve their services, depending on the terms and settings you’ve agreed to. It’s essential to verify the service terms, privacy settings, and data retention policies of any AI tool before use. Moreover, certain types of data, such as passwords, health information, financial details, and personal data of third parties, should never be entered into an AI system without appropriate safeguards and authorizations.
To navigate these complexities, this article will cover several key areas:
- Understanding AI and Privacy: An Introduction
- What Happens to Your Data in AI Systems?
- Variations in Data Handling Across Different AI Services
- Best Practices for Protecting Personal Data in AI Interactions
- AI and GDPR: Ensuring Compliance and Safeguarding Privacy
By the end of this discussion, you’ll have a clearer understanding of the potential risks and best practices associated with using AI technologies, ensuring that your data remains secure and your privacy intact.
Understanding AI and Privacy: An Introduction
When we interact with artificial intelligence (AI) systems, whether it’s entering an email into a chatbot, summarizing a contract, or uploading a medical report, we often do so without a clear understanding of what happens to the data we enter. This data can include personal details, confidential information, or data belonging to third parties, all of which are subject to privacy concerns and regulations.
What Happens to Your Data?
Once data is entered into an AI system, several processes take place:
- Transmission: Data is sent to the provider’s systems, often over the internet.
- Processing: AI algorithms process the data to generate the necessary response or service.
- Storage: Data may be stored in the form of conversations, logs, or other formats for varying durations.
- Improvement of Services: Some services use the data to refine and improve their algorithms, depending on their terms and privacy settings.
- Access by Third Parties: Data might be accessible by integrated services or providers involved in the processing chain.
- Deletion or Retention: Data is either deleted or retained according to the provider’s policies and applicable legal requirements.
It’s crucial to understand that not all AI tools handle data in the same way. Differences often exist between free consumer services and professional or business plans, between services accessed via APIs and those executed locally on your device.
Content to Avoid Entering
Certain types of content should never be entered into an AI system without appropriate authorizations and protections. This includes passwords, health data, financial information, confidential documents, and personal data of clients or colleagues. The inadvertent sharing of such sensitive information can lead to significant privacy breaches and legal repercussions.
Before using any AI service, it is advisable to review the terms of service, privacy settings, and data retention policies to understand how your data will be handled and protected. This proactive approach helps mitigate risks and ensures compliance with privacy laws like the GDPR, which emphasizes data minimization, transparency, and the purpose of processing.
What Happens to Your Data in AI Systems?
When you enter data into an AI system, such as typing an email into a chatbot, summarizing a document, or inputting personal information, several processes occur behind the scenes. Understanding these processes is crucial for safeguarding your privacy and ensuring compliance with data protection regulations like the GDPR.
Transmission and Processing of Data
Initially, the data you enter is transmitted to the AI provider’s systems. This transmission is typically secured through encryption to protect the data from unauthorized access during transit. Once received, the AI system processes the data to perform the requested service, such as generating a summary or correcting grammar.
Storage and Use of Data
After processing, the data may be stored in the provider’s systems. This storage can include not only the original data but also metadata and logs of the interaction. Providers might use this stored data to improve their AI models, depending on their privacy policy and your settings. It’s essential to review these policies to understand how your data is being used and retained.
Access by Third Parties
In some cases, third-party services integrated with the AI system might access your data. This integration can help enhance the functionality of the AI service but also raises additional privacy concerns. Ensure that these third-party services comply with strict data protection standards.
Deletion and Retention
The retention period for your data can vary based on the provider’s policy and the legal framework. Some data might be deleted immediately after processing, while other data may be retained for a specified period for compliance or business reasons. Confirm the data retention practices of the AI service to ensure they align with your privacy expectations and legal obligations.
Differences in Data Handling
Not all AI tools handle data the same way. Differences can exist between free consumer services and professional or business offerings, including how data is processed, stored, and deleted. Services accessed via APIs or those executed locally on your device may also handle data differently. Always verify the specific practices of the service you are using.
Variations in Data Handling Across Different AI Services
When engaging with different AI services, it’s crucial to understand that not all handle data in the same way. The variations often depend on the nature of the service, whether it’s free or paid, and the specific configurations set by the user or the organization.
Consumer vs. Professional Services
Free AI services, typically aimed at consumers, may not offer the same level of data protection as services designed for business use. Professional services often provide enhanced security features and clearer data handling policies, reflecting their use in environments where data sensitivity is a priority.
APIs vs. Local Execution
Using AI through APIs means data is sent to and processed on external servers, whereas models executed locally handle data within the user’s device. This distinction is critical for assessing the risk of data exposure.
Service-Specific Policies
Each AI service has its own set of policies regarding data retention, deletion, and usage for service improvement. Users must review these policies to understand how their data is treated post-interaction. For instance, some services might store interactions to refine AI models, while others might offer options to limit data retention.
It is essential for users to verify the terms of service, privacy settings, and retention policies of each AI tool they use to ensure compliance with their data security standards and regulatory requirements.
Best Practices for Protecting Personal Data in AI Interactions
When engaging with AI technologies, safeguarding personal and sensitive data is paramount. Here are some practical steps to ensure data security and compliance with privacy standards like the GDPR.
Minimize Data Exposure
- Remove personally identifiable information such as names, addresses, and social security numbers from data sets before processing with AI.
- Share only the minimal amount of data necessary for the AI to perform its task.
Use Organization-Approved Tools
Always opt for AI tools and services that have been vetted and approved by your organization to avoid potential security vulnerabilities.
Adjust Privacy Settings
Review and configure the privacy settings of AI services to control the extent of data collection and its usage. This includes settings related to data history and usage logs.
Understand Data Retention and Deletion Policies
- Verify how long the AI service retains data and how it is deleted. Ensure these practices align with legal requirements and organizational policies.
- Check who has access to the data and under what circumstances.
Avoid Mixing Personal and Work Data
Do not use personal accounts or tools for work-related tasks involving sensitive data. This helps in maintaining clear boundaries between personal and professional data handling.
Implement Internal Guidelines and Training
Develop and enforce internal policies regarding the use of AI tools. Regular training sessions for staff can help in understanding the risks and best practices related to AI and privacy.
AI and GDPR: Ensuring Compliance and Safeguarding Privacy
When integrating AI technologies into business processes, understanding and adhering to the General Data Protection Regulation (GDPR) is crucial. GDPR sets guidelines for the collection and processing of personal information of individuals within the European Union (EU) and the European Economic Area (EEA). It emphasizes principles like data minimization, transparency, and the purpose of processing, which are essential when dealing with AI and privacy.
Data Minimization
Data minimization refers to the principle that organizations should collect and process only the data absolutely necessary for the completion of its business purposes. In the context of AI, this means training models on no more data than is required, and ensuring that personal data is not used unless absolutely necessary.
Transparency and Purpose of Processing
Transparency in AI implies that users are fully informed about how their data is being used. AI systems should clearly disclose the purpose of data collection and processing. This aligns with GDPR’s requirement that the processing purposes must be specified, explicit, and legitimate. Ensuring that users understand what happens to their data and why it is being collected is a fundamental step in safeguarding privacy.
Protecting Information
Under GDPR, protecting the integrity and confidentiality of personal data is paramount. This involves implementing appropriate technical and organizational measures to ensure data security, including protection against unauthorized or unlawful processing, accidental loss, destruction, or damage. AI systems must be designed with robust security features to prevent data breaches and leaks.
Adhering to these GDPR principles not only helps in compliance but also builds trust with users by ensuring that their personal data is handled responsibly and ethically in the realm of artificial intelligence.
